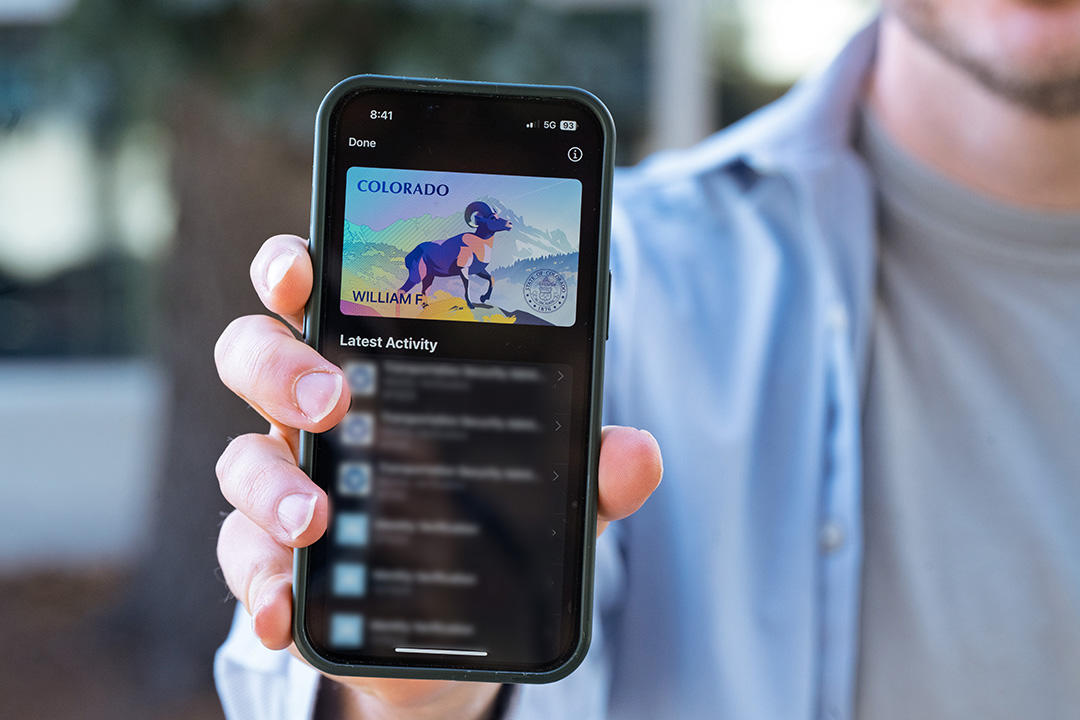
A draft report from the National Institute of Standards and Technology is aimed at a practical bottleneck for mobile driver’s licenses: even where the digital IDs exist, relatively few online services accept them.
In an announcement published Nov. 19, NIST said its National Cybersecurity Center of Excellence published a draft report titled "Digital Identities — Mobile Driver’s License (mDL): Enabling Secure and Interoperable Online Use" (NIST Special Publication 1800-42). The agency said the document is meant to help organizations judge whether they can integrate mDLs with their existing systems and, if so, how to do it.
According to NIST, 22 U.S. states and territories now have active mDL programs. Across those programs, the agency said, at least 5 million mDLs are in use in the United States, and approximately 47% of the population has access to them.
The agency described the gap as an ecosystem problem rather than a lack of core technology. In NIST’s account, consumers have less reason to adopt mDLs if they are not widely accepted for common, high-value uses, while companies may be reluctant to invest in support before enough customers demand it.
What NIST says the project built
NIST said the project involved tech firms, public agencies and five of the 10 largest U.S. banks. According to the agency, the resulting reference architecture demonstrates three functions: presenting an mDL during online identity verification; requesting and presenting an mDL again in some higher-risk situations, such as larger-value transactions or account recovery; and issuing a phishing-resistant authenticator, or passkey, to a user.
NIST said the demonstration relied on existing commercial technology, software and standards. The point, the agency said, was to show that organizations could begin implementing mDL support now with relatively little difficulty.
The draft also covers threats to an mDL ecosystem and possible risk mitigations, according to NIST. The announcement says it points readers to other NIST publications, including the NIST Privacy Framework and NIST Special Publication 800-53 revision 5, for security and privacy controls.
What the evidence supports — and what it does not
The announcement presents the report as implementation guidance, not as evidence that mDL acceptance is already broad online. NIST said only a small number of online service providers accept mDLs today.
It also says the report includes seven best practices on user experience, drawn from patterns observed during usability testing with volunteers. In the announcement, however, NIST did not provide the number of volunteers or detailed performance results from that testing.
NIST said the initial demonstration use case involved financial institutions, but the agency added that the report is intended to be useful for any organization that currently accepts physical IDs and wants to accept mDLs. Examples named in the announcement include access to healthcare information and interactions with state and federal government services.
For now, the report remains a draft. NIST said it is accepting public comments through Dec. 20, 2026, by email or through the project’s resource hub page.